apache / apache/incubator-seata
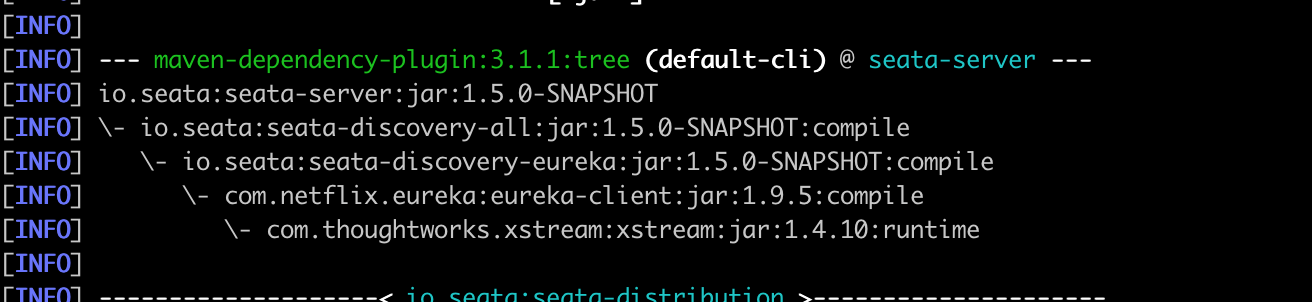
XStream 远程代码执行漏洞,建议升级
Open
- Dominant language
- Java
- Stars
- 26k
- Forks
- 8.8k
- Avg merge
- 1d 8h
- Merged PRs (30d)
- 4
Description
Contributor guide
Research direction
The issue identifies an XStream remote-code-execution vulnerability and recommends upgrading, but provides no affected version, target file, dependency entry, or test. Start by reviewing the attached image and locating the project's XStream dependency; done should mean the vulnerable dependency is upgraded and the relevant security behavior is verified.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- java
- Domain
- security
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 20/100