Hide Plaintext Passwords Druid cachedNamespace Lookups - Druid UI
- Dominant language
- Java
- Stars
- 14.1k
- Forks
- 3.8k
- Avg merge
- 2d 58m
- Merged PRs (30d)
- 233
Description
### Motivation
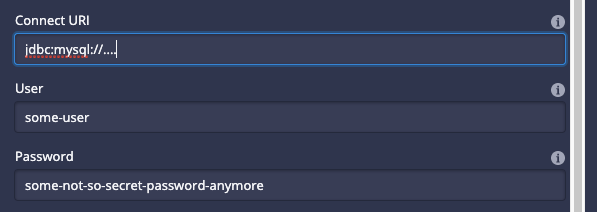
Currently when pushing a cachedNamespace lookup, the password for the **JDBC** source is exposed, in plaintext in the lookups Apache Druid UI.
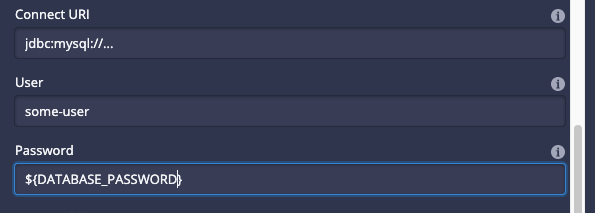
Would like it to look like this instead:
### Proposed changes
I would like to be able to mask this value, how? I am not sure, if it was possible to add an `env` into the `JSON` like:
```json
{
"type": "cachedNamespace",
"extractionNamespace": {
"type": "jdbc",
"connectorConfig": {
"connectURI": "jdbc:mysql://dburl:port/db?useSSL=false",
"user": "some-user",
"password": "${DATABASE_PASSWORD}",
"createTables": false
},
"table": "some-table",
"keyColumn": "some-key-column",
"tsColumn": "some-ts-column",
"valueColumn": "some-value-column",
"namespace": "default"
},
"firstCacheTimeout": 12345678,
"injective": true
}
```
### Rationale
This would be simple since, then while deploying druid, you simply attach this `env` which can be fetched in a secure way.
For instance with `k8s` within a `STS` or `deployment` file::
```yaml
- name: DATABASE_PASSWORD
valueFrom:
secretKeyRef:
key: password
name: db-secret
```
### Operational impact
Make passwords more protected.
Contributor guide
Research direction
No source files, tests, or entry points are named. Start by locating the Druid UI rendering for cachedNamespace JDBC connectorConfig and tracing how the password reaches that view; define completion as preventing plaintext password display and clarify whether environment-variable substitution is also required.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- java, kubernetes, mysql
- Domain
- databases, frontend, security
- Issue type
- Feature
- Difficulty
- 5/5
- Estimated time
- Over a week
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100