@actions/github latest version includes many vulnerabilities detected by Dependabot
Nobody has claimed this yet.
- Dominant language
- TypeScript
- Stars
- 5.9k
- Forks
- 1.8k
- PR merge metrics
- No merged PRs in 30d
Description
"@actions/github": "^5.1.1", latest, includes many vulnerabilities detected by Dependabot. They are introduced in the @octokit, node-fetch, deprecation and the universal-user-agent submodules.
Please upgrade to latest version (or at least to the ones without these vulnerabilities)
Screenshots
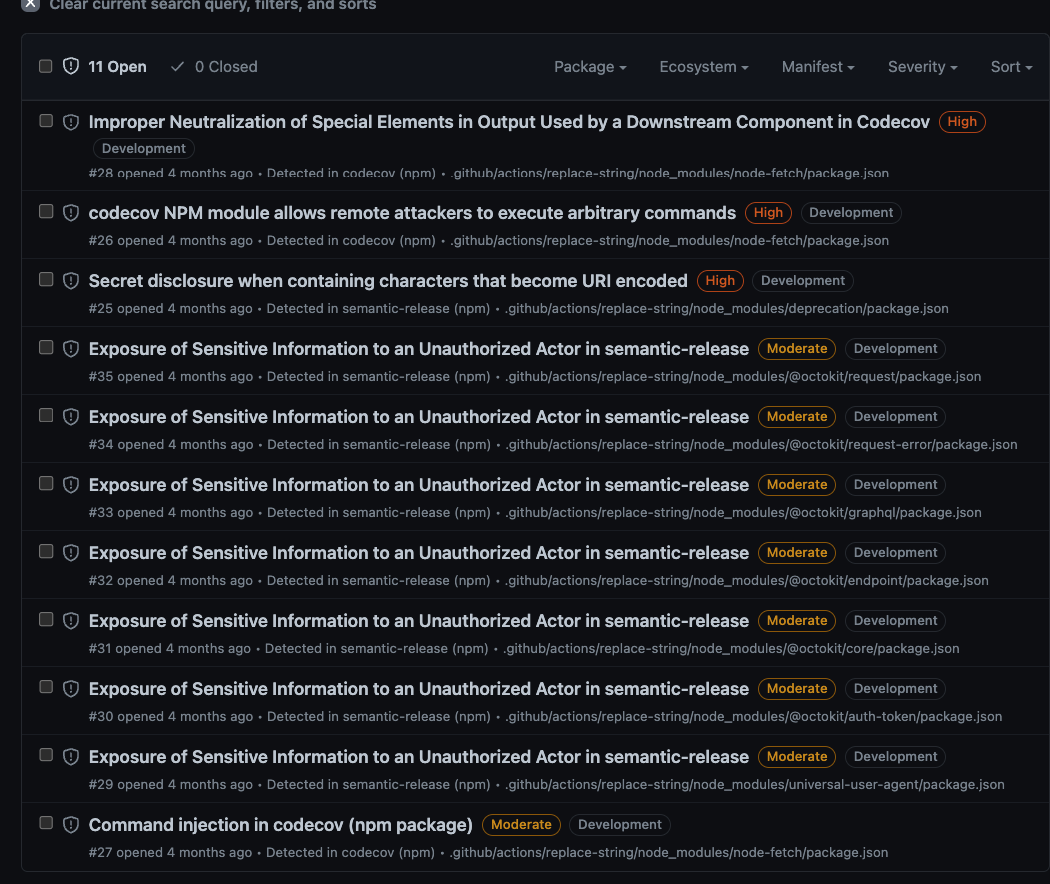
Additional context
My action package.json dependencies:
"dependencies": {
      "@actions/core": "^1.10.0",
      "@actions/github": "^5.1.1"
  }
Contributor guide
First steps
- Read the whole issue, then the project's contributing guide.
- Comment on the issue to say you are picking it up — it saves two people doing the same work.
- Fork the repository and make your change on a branch.
- Open a pull request that references the issue number.
Research direction
Start with the repository's package.json and inspect the @actions/github dependency and its transitive @octokit, node-fetch, deprecation, and universal-user-agent packages. Compare the dependency tree with the reported Dependabot vulnerabilities and verify that the updated dependency versions no longer trigger those findings.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- github, typescript
- Domain
- devops, security
- Issue type
- Bug
- Difficulty
- 2/5
- Estimated time
- 1-3 hours
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 35/100