spring security url 조건 *필독*
Open
- Dominant language
- Jupyter Notebook
- Stars
- 0
- Forks
- 0
- PR merge metrics
- No merged PRs in 30d
Description
[
](url)
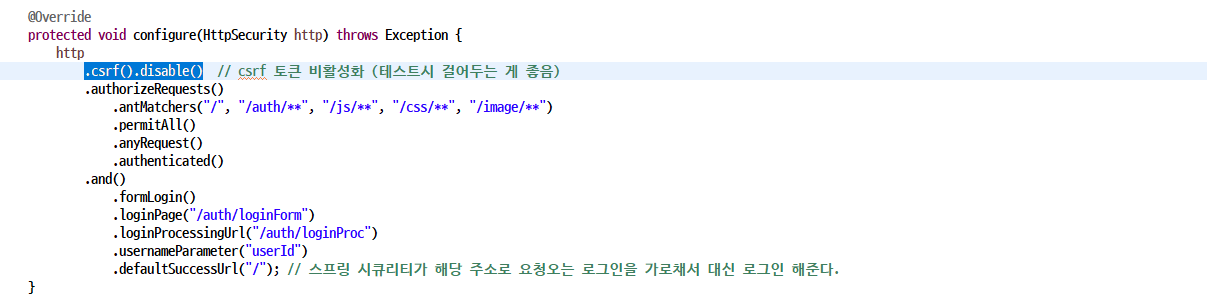
.antMatchers() <= 이 안에 들어간 url 은 권한이 없어도(로그인이 안되어있어도) 들어갈 수 있는 페이지 입니다!
"/{권한여부}/{서비스}/{기능}"
ex) 로그인페이지 이동 url : "/auth/loginForm"
/auth( 권한이없어도 가능하니 필수)
/user(유저서비스이지만 공통부분이라 생략)
/loginForm(기능)
Contributor guide
No contributing guide indexed for this repository
Research direction
No source file or test is named; start by reviewing the .antMatchers() URL rule and the access-path examples in the issue. Done would require a clearly identified documentation change that explains the URL permission convention and its login-page example.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- spring
- Domain
- authentication, authorization, security
- Issue type
- Documentation
- Difficulty
- 1/5
- Estimated time
- Under an hour
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 30/100