GoogleCloudPlatform / GoogleCloudPlatform/esp-v2
Accessing JWT tokens in cookies
- Dominant language
- Go
- Stars
- 307
- Forks
- 185
- Avg merge
- 14h 45m
- Merged PRs (30d)
- 6
Description
I am using a JS SPA frontend which talks to the API backend via Endpoints (ESPv2) hosted on Cloud Run. ESPv2 invokes the Cloud Run backend via native GCP IAM. All user requests go through a load balancer that routes according to path, so the domain is common to all components from the end user's perspective.
We would like to be able to store and transmit JWT tokens with cookies.
The frontend directs an unauthenticated user to login to Azure AD and receives a token back. For the frontend to allow the user to get a request through ESPv2, the token needs to be in an HTTP header ('Authorization: ' as usual).
But this requires that on the user end the token is stored in the browser's localStorage (or sessionStorage) which is generally considered bad practice. We want to store the token in cookies so that we can set httpOnly, secure and sameSite flags.
Is there a way (or could a way be created) for ESPv2 to _instead_ parse the cookies to look for a token in particular cookie key? Our frontend framework allows this, but it doesn't work with our implementation of Endpoints.
EG I'm thinking extended x-google-jwt-locations to something like below
```
x-google-jwt-locations:
- header: "Cookie"
value_prefix: "Bearer "
cookie-key: "auth._token.aad"
```
Which would find the JWT token in amongst the below (shortened, redacted) sample cookies:
```
auth._token.aad=Bearer%20; auth._token_expiration.aad=1646369191000; auth.strategy=aadAP
```
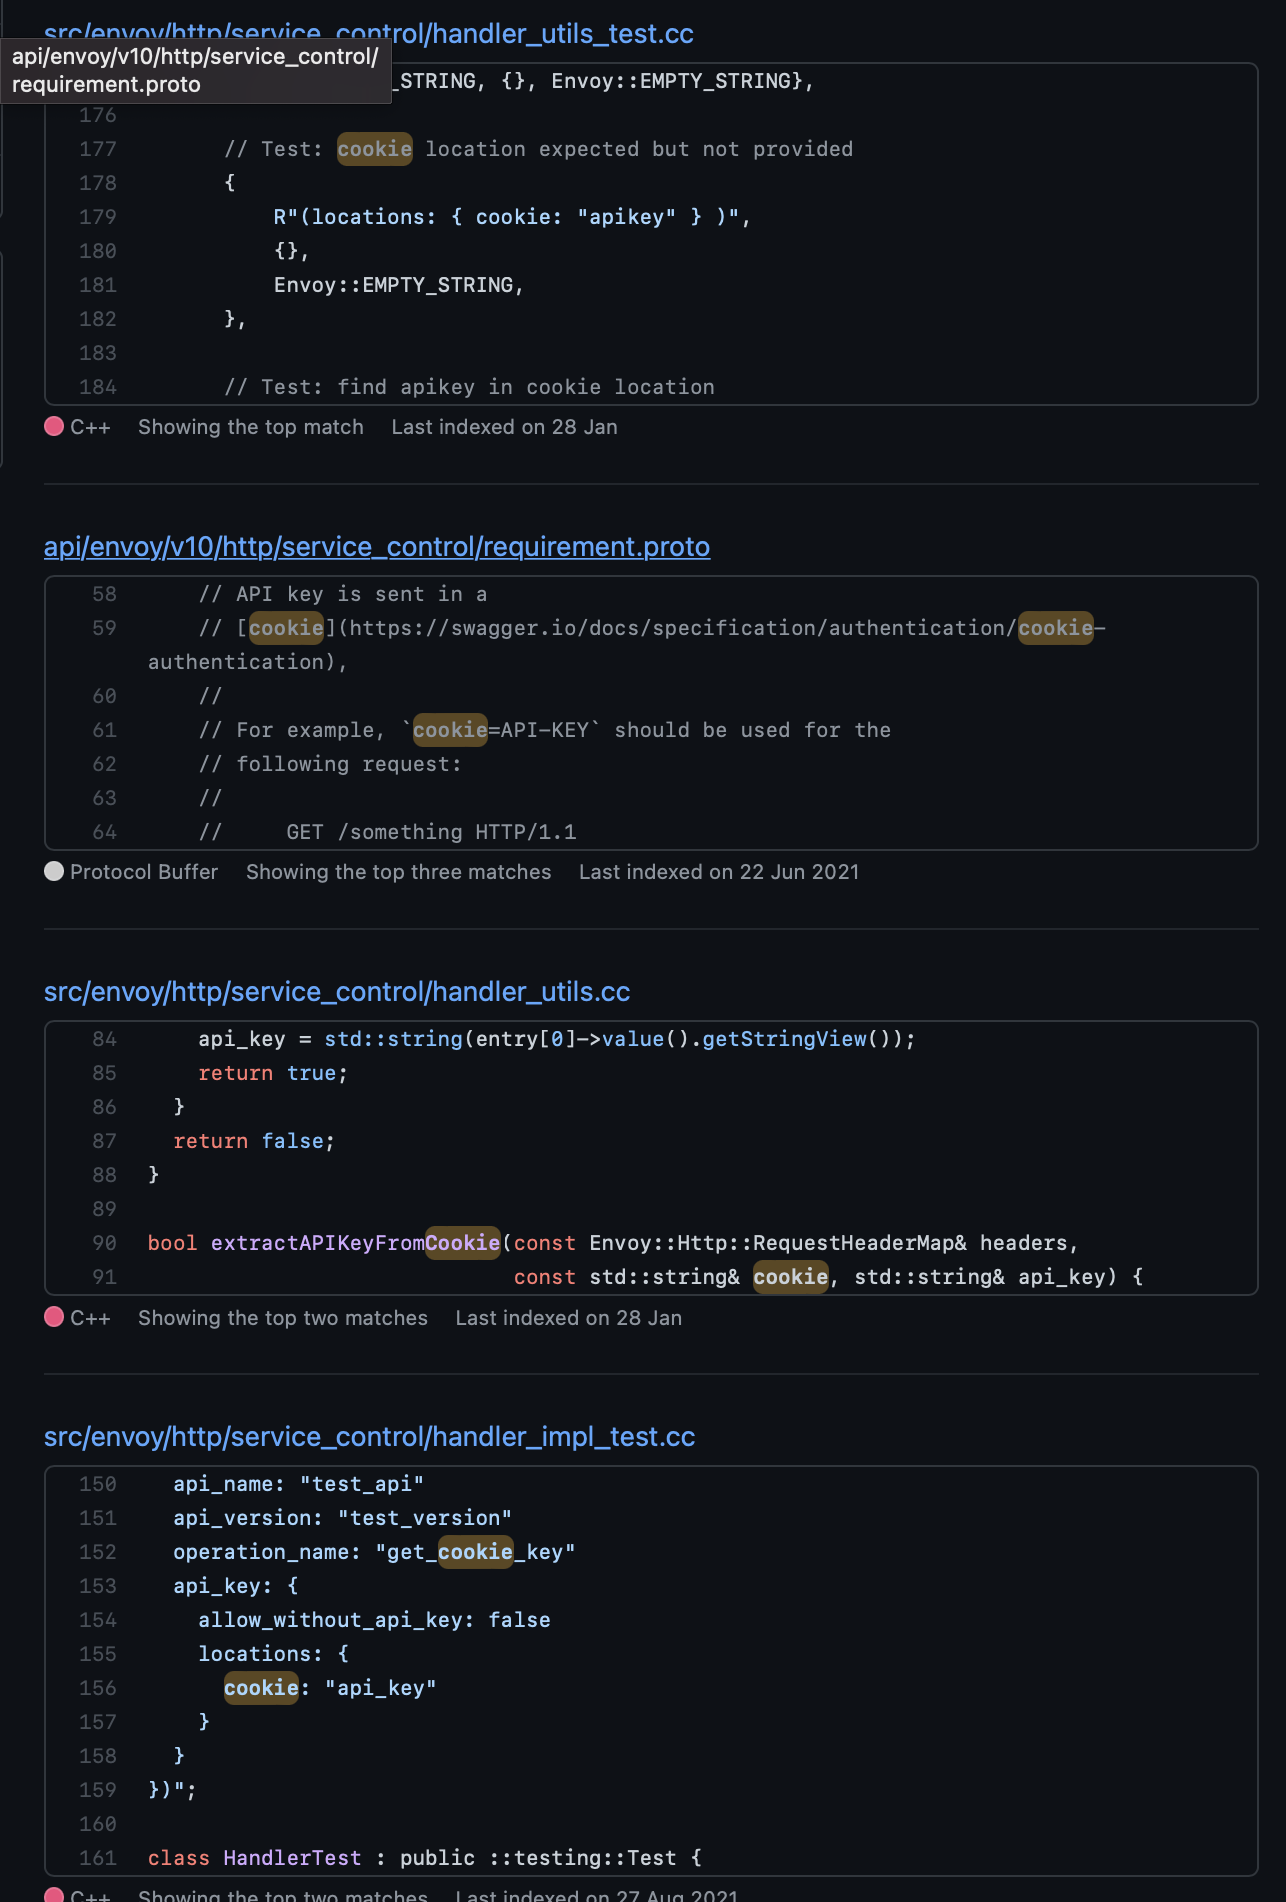
PS I noticed there's already some parsing of cookies for API keys - maybe that could be extended to extract other keys?
Contributor guide
Assessment
This issue has not been assessed yet.