Gallopsled / Gallopsled/pwntools
`elf.sym['read']` gives an incorrect address on Ubuntu 20.04.3 LTS with gcc 9.3.0
- Dominant language
- Python
- Stars
- 13.7k
- Forks
- 1.9k
- Avg merge
- 6d 23h
- Merged PRs (30d)
- 3
Description
## Environment
| Name | Version |
| --- | --- |
| OS | **Ubuntu 20.04.3 LTS (focal)** |
| Pwntools | **4.6.0** |
| gcc | **9.3.0-17ubuntu1~20.04** |
| GNU ld | **2.34** |
I compiled the following program using `gcc 9.3.0` (the default one on Ubuntu 20.04.3 LTS).
```c
#include
int main() {
// no brute forcing
sleep(3);
// exploit me
char buf[4];
read(0, buf, 0x100);
}
```
Here's the problem:
* pwntools: `hex( ELF('./unexploitable').sym['read'] )` gives `0x401054`
* gdb: `read@plt` is at `0x401050`
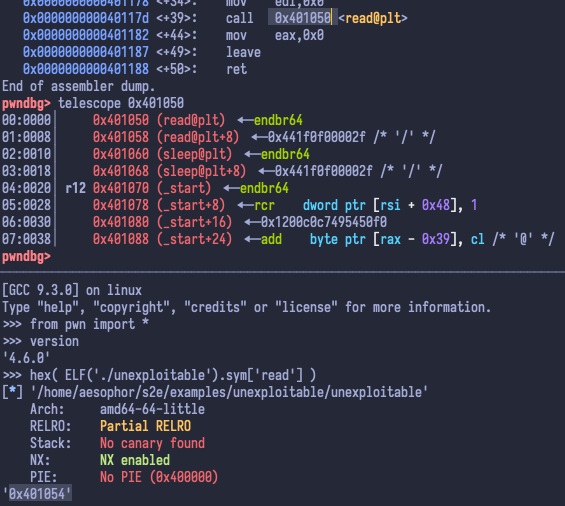
However, I also compiled this program on Arch Linux using `gcc 11.1.0` and the result is correct.
This erroneous result only happens on **Ubuntu 20.04.3 LTS** with **gcc 9.3.0**
---
The source, makefile and the compiled executable is provided in this zip file: [unexploitable.zip](https://github.com/Gallopsled/pwntools/files/7315310/unexploitable.zip)
Contributor guide
Research direction
Start by reproducing the discrepancy with the attached unexploitable.zip under Ubuntu 20.04.3 LTS, then compare pwntools' elf.sym['read'] result with gdb's read@plt address. Done means the symbol lookup returns the correct address for this executable without regressing the working Arch Linux case.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- c, linux, python
- Domain
- operating-systems, reverse-engineering
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 32/100