DependencyTrack / DependencyTrack/dependency-track
A project component that was marked as vulnerable retains the same vulnerability and risk score when re-measured, even if the vulnerability in that component is no longer present or the risk score has changed
- Dominant language
- Java
- Stars
- 4.2k
- Forks
- 811
- Avg merge
- 8h 39m
- Merged PRs (30d)
- 237
Description
### Current Behavior
A project component that was marked as vulnerable retains the same vulnerability and risk score when re-measured, even if the vulnerability in that component is no longer present or the risk score has changed.
**Possible reason:** once a component has been scanned, it is never scanned again. Each component has its own unique `Object Identifier,` which dependency-track assigns to it itself without being able to change. Perhaps, having scanned a components once, the scanner no longer scans components with the same `Object Identifier`. I tried manually changing the hash sums of a component in the bom file, but if the version and name of the component hasn't changed - then its `Object Identifier` won't change either after uploading modified bom. But when upload a component with a new version or removing the old one and upload the same one again, the `Object Identifier` will be different and it will give the actual result
### Steps to Reproduce
Scenario 1:
1. Create a component in the project (or load a bom file with the component) (e.g. com.fasterxml.jackson.core/jackson-core@2.10.1)
2. Initialize the project measurement manually or wait until it happens automatically
3. Discover a vulnerable component, examine its vulnerabilities and risk score
4. Wait for a significant amount of time
5. Upload a new bom file (assuming that the vulnerable component remains the same version as before) or just re-initialize the project measurement manually or wait until it happens automatically.
Even if a component is no longer vulnerable or its risk score has changed, it will still have the same vulnerabilities and the same risk score in this project. This can be observed by creating this component in a new project or by uploading a bom file with this component to a new project.
Old project after re-measurement or update bom with same component version

New project with same component

Scenario 2:
1. Create a component in the project (or load a bom file with the component) (e.g. org.springframework/spring-core@6.0.7)
2. Manually change the version and purl of the component (from 6.0.7 to 6.0.8)
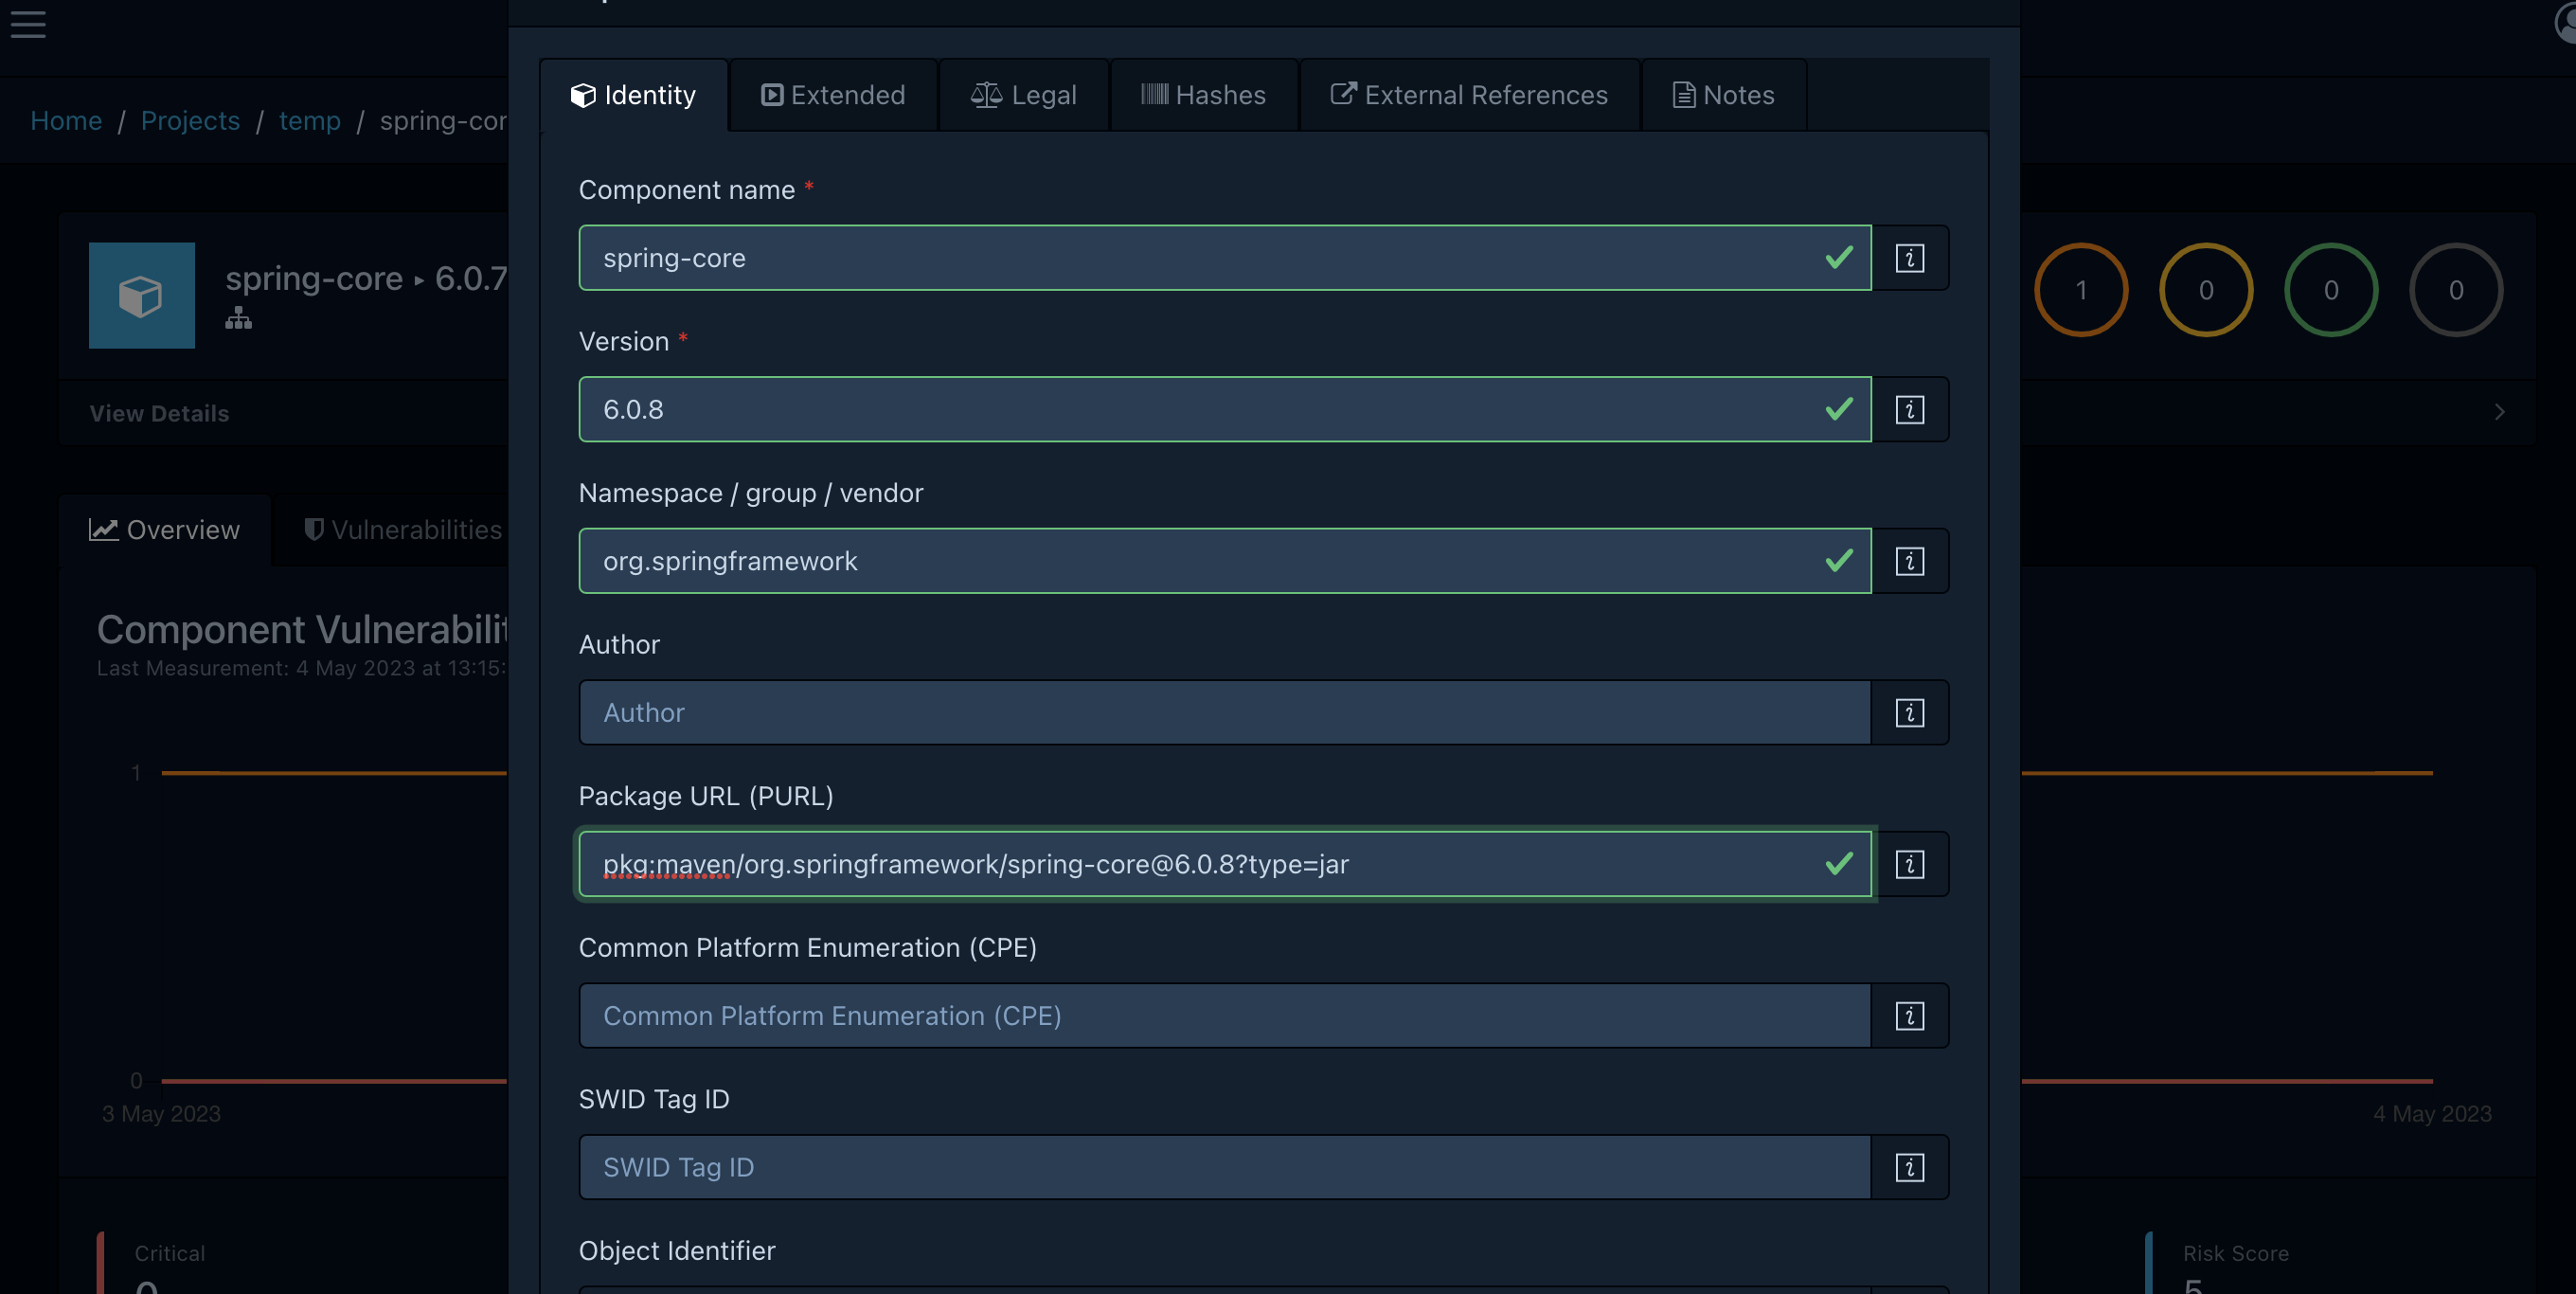
3. Initialize the project measurement manually or wait until it happens automatically
4. Optional: upload a new bom file with a new version of the component (in our case it is org.springframework/spring-core@6.0.8
As we can see, the version of the component has been updated, but the vulnerabilities remain from the previous version. Even if the new component is not vulnerable or has a different risk score, it will still have the same vulnerabilities and the same risk score in this project. This can be observed by creating this component in a new project or by uploading a bom file with this component to a new project.
Old project with 6.0.7

Old project after manual change version from 6.0.7 to 6.0.8, re-measurement and (optional: upload new bom with new 6.0.8 component version)

6.0.8 in new project

### Expected Behavior
The re-scan must be performed for all components, regardless of whether they have already been scanned before and whether they have been changed
### Dependency-Track Version
4.8.0
### Dependency-Track Distribution
Container Image
### Database Server
H2
### Database Server Version
_No response_
### Browser
N/A
### Checklist
- [X] I have read and understand the [contributing guidelines](https://github.com/DependencyTrack/dependency-track/blob/master/CONTRIBUTING.md#filing-issues)
- [X] I have checked the [existing issues](https://github.com/DependencyTrack/dependency-track/issues) for whether this defect was already reported
Contributor guide
Assessment
This issue has not been assessed yet.