DependencyTrack / DependencyTrack/dependency-track
One component version shows a vulnerability in one project but not in the second project
- Dominant language
- Java
- Stars
- 4.2k
- Forks
- 811
- Avg merge
- 8h 39m
- Merged PRs (30d)
- 237
Description
The defect may already be reported! Please search for the defect before creating one. Done
### Current Behavior:
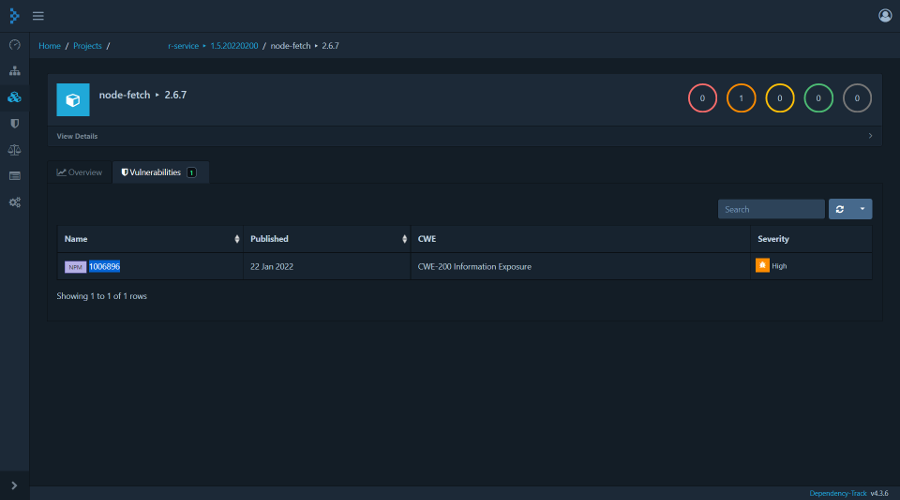
- We have a project which is using node-fetch 2.6.7.
- We imported a SBoM to this project with version 1.5.20220200
- Dependency Track showed the vulnerability [1006896](https://dtrack.compart.com/vulnerabilities/NPM/1006896)
- In the meanwhile, the [CVE-2022-02359]#8https://nvd.nist.gov/vuln/detail/CVE-2022-0235#VulnChangeHistorySection) changed. With this change was node-fetch version 2.6.7 excluded
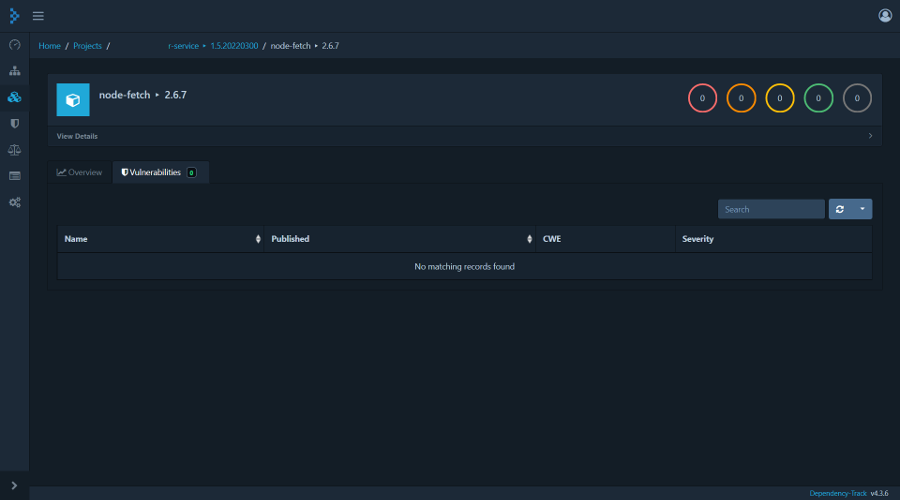
- We imported a SBoM to this project with version 1.5.20220300
- This time we didn't see the vulnerability 1006896
Currently, we have two different results in Dependency Track for this node-fetch 2.6.7 depending on the version of our project
### Steps to Reproduce:
I have no idea, how to reproduce it.
### Expected Behavior:
The same component/version combination shall always show the same vulnerabilities independent of the project/version
### Environment:
- Dependency-Track Version: 4.3.6
- Distribution: Docker
- BOM Format & Version: CycloneDX 1.2
- Database Server: PostgreSQL
- Browser: Chrome
### Additional Details:
Project as version 1.5.20220200 **with** vulnerability in component node-fetch 2.6.7
Project as version 1.5.20220300 **without** vulnerability in component node-fetch 2.6.7
Contributor guide
Research direction
Start by comparing the two CycloneDX 1.2 SBOM imports for node-fetch 2.6.7 and inspect how vulnerability 1006896, tied to CVE-2022-02359, is associated with each project version. Reproduce the differing results in Dependency-Track 4.3.6 with PostgreSQL; done means the same component/version combination consistently reports the same vulnerability.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- java, node.js, postgresql
- Domain
- backend, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 25/100