ConsenSysMesh / ConsenSysMesh/Stow-Smart-Contracts
Linnia Smart Contracts Security Bounties
- Dominant language
- JavaScript
- Stars
- 55
- Forks
- 33
- PR merge metrics
- No merged PRs in 30d
Description
The scope of this bounty is for bugs in the Linnia Smart Contracts, whose severity is judged by the OWASP model:
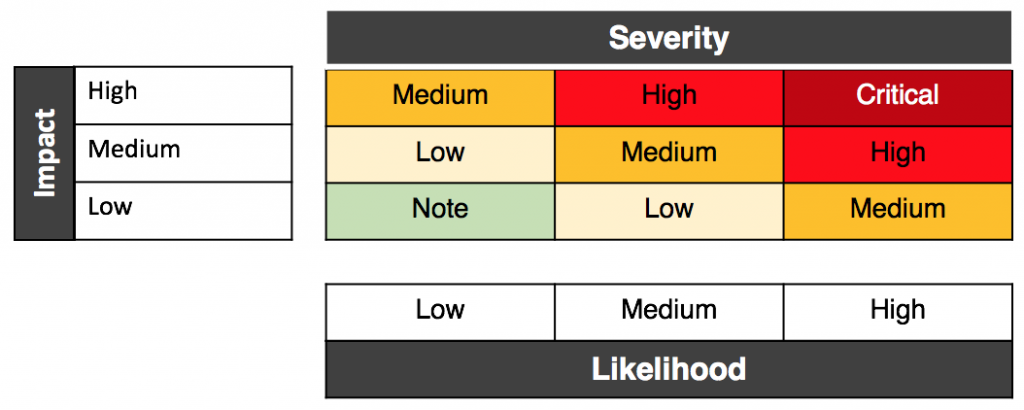
Payouts will be as follows:
Critical: .2 ETH
High: .15 ETH
Medium: .05 ETH
Low: .02 ETH
Note: At discretion of Linnia team.
Payouts will be made to the first individuals who report bugs, and exploits will be ineligible for payouts if they've already been used on the deployed contracts.
Non-security critical severity issues (style issues, gas optimizations, storage optimizations) are not eligible for this bounty.
Determinations of eligibility and all terms related to this award are at the sole and final discretion of the Linnia team.
Contributor guide
No contributing guide indexed for this repository
Research direction
The issue provides only the bounty terms and an OWASP severity reference; it names no source files, tests, entry points, or reproducible defect. Review the smart-contract code and its existing security context first; done would require reporting a previously unused security bug that the Linnia team accepts as eligible.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- javascript
- Domain
- blockchain
- Issue type
- Bug
- Difficulty
- 5/5
- Estimated time
- Over a week
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 15/100