Static Web Apps Password screen does not currently send back Strict-Transport-Security Header, it should
- Dominant language
- No language data
- Stars
- 346
- Forks
- 67
- PR merge metrics
- No merged PRs in 30d
Description
**Is your feature request related to a problem? Please describe.**
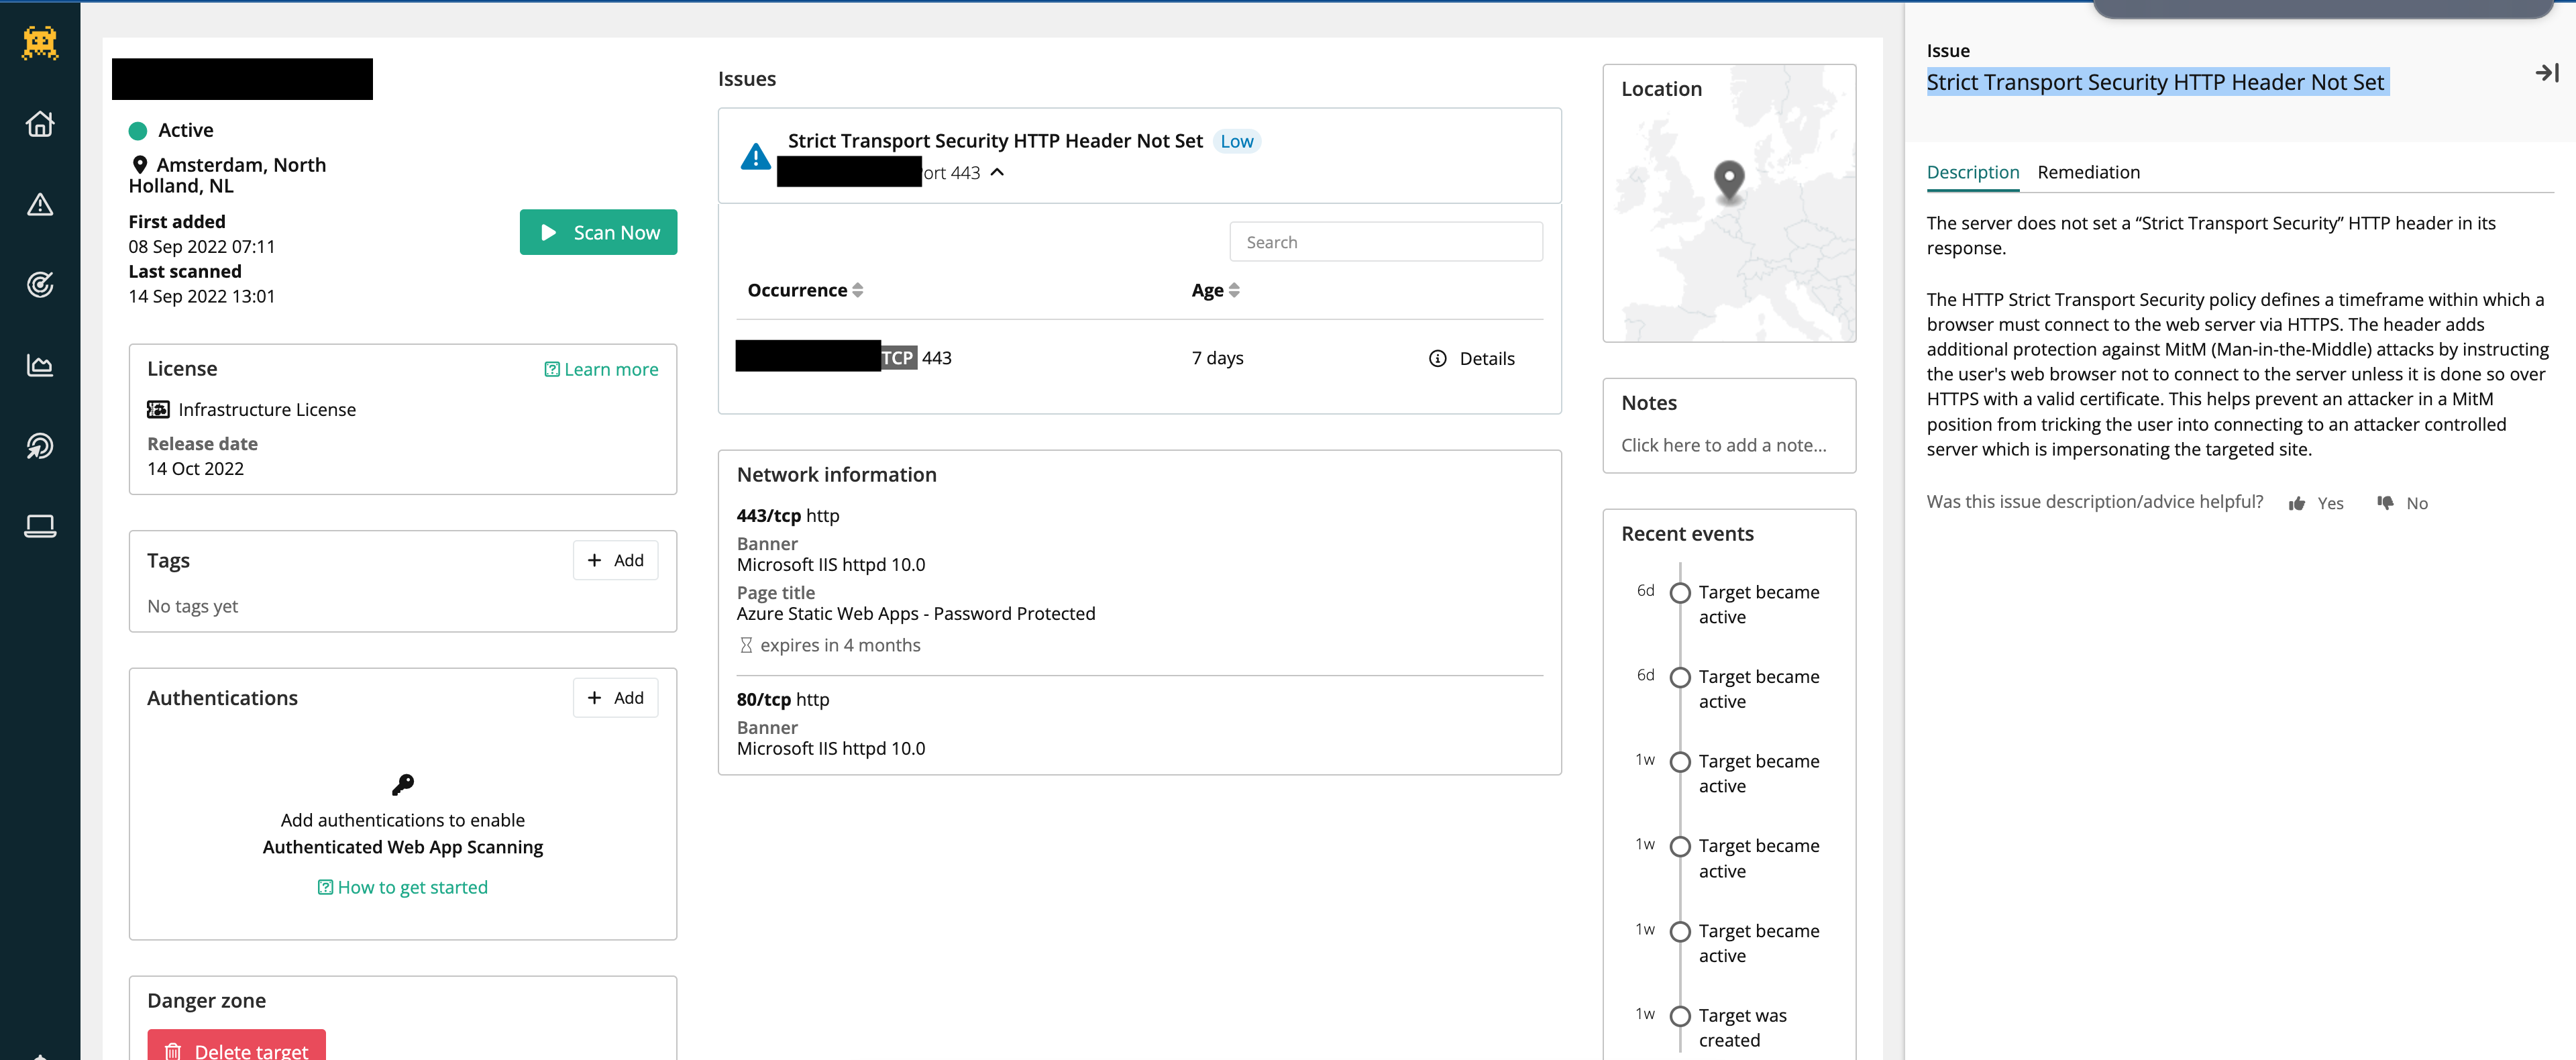
I ran automated security platform intruder.io against my static web apps, and the only issue picked up was this low priority one. It seems like an easy, but low priority win so thought I'd list it here rather than as a 'vulnerability'. I can't affect the headers that the SWA-provided password screen sends back and it'd be great to be able to show to customers that we pass every single security check rather than have one small hanger on!
**Describe the solution you'd like**
When a password screen is enabled (use https://staging.zeti.co.uk/ as an example) it should return a Strict-Transport-Security header. It already does when a password screen is not enabled.
**Describe alternatives you've considered**
Ignoring the issue. But to be honest that's a path that we'd rather not walk down if possible as it can get risky.
**Additional context**
Add any other context or screenshots about the feature request here.
Contributor guide
No contributing guide indexed for this repository
Assessment
This issue has not been assessed yet.