Completions for the `getSecret` method are shown in context where they are not valid
- Dominant language
- Bicep
- Stars
- 3.6k
- Forks
- 830
- Avg merge
- 1d 2h
- Merged PRs (30d)
- 79
Description
**Bicep version**
Latest in `main`
**Describe the bug**
Completions for the `getSecret` method are shown in context where they are not valid.
**To Reproduce**
Steps to reproduce the behavior:
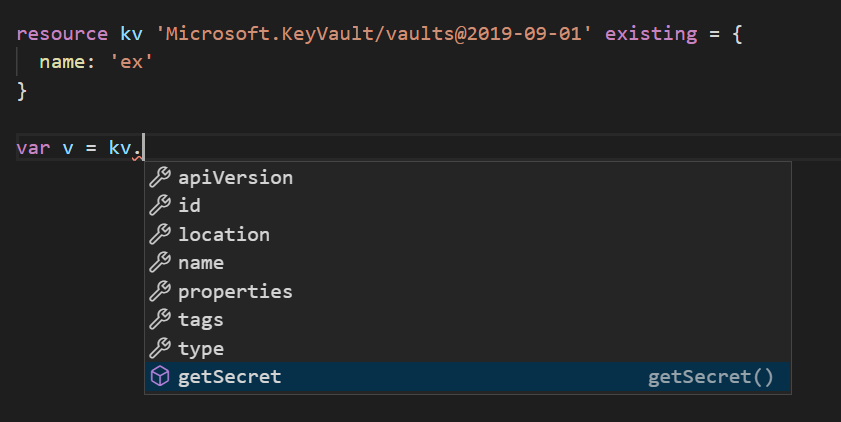
After committing the completion, you get the following error immediately:
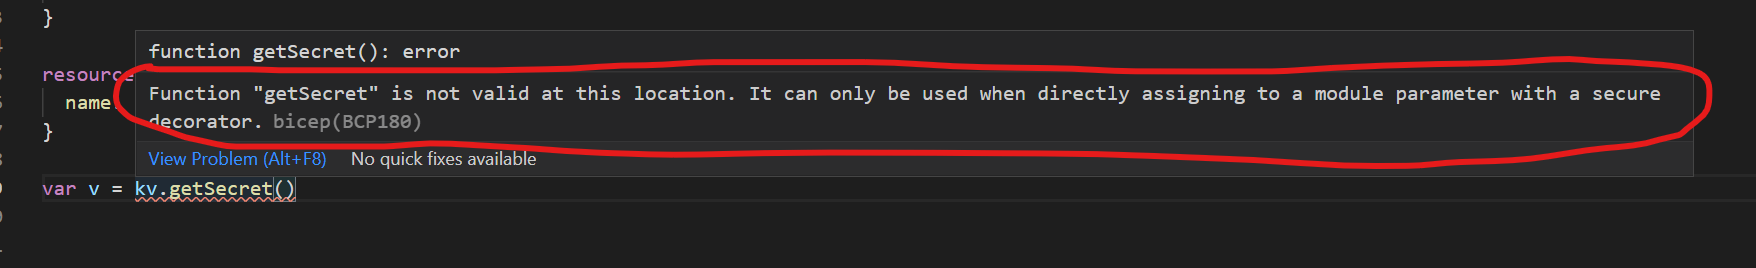
**Additional context**
I think we should account for function placement flags when offering this completion so it doesn't show up in invalid contexts. However, I think it's ok to offer this completion on module params that aren't tagged as secure. It's possible the user is refactoring and just hasn't tagged them as secure.
Contributor guide
Research direction
Reproduce the invalid getSecret completion in the latest Bicep main build, then locate the completion logic that offers this method and inspect how function placement flags are handled. Done means getSecret is not offered in invalid contexts while remaining available for permitted module parameters, including those without a secure tag.
Written by the indexing model from the issue text.
Assessment
- Domain
- tooling
- Issue type
- Bug
- Difficulty
- 3/5
- Estimated time
- 1-2 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 42/100