Azure / Azure/azure-functions-host
`SetIsOriginAllowedToAllowWildcardSubdomains()` support in the App Service Portal's CORS blade.
- Dominant language
- C#
- Stars
- 2k
- Forks
- 482
- Avg merge
- 2d 12h
- Merged PRs (30d)
- 38
Description
This issue is an extension of #620 based on [this comment ](https://github.com/Azure/azure-functions-host/issues/620#issuecomment-428043811).
I need to enable [.SetIsOriginAllowedToAllowWildcardSubdomains();](https://docs.microsoft.com/en-us/dotnet/api/microsoft.aspnetcore.cors.infrastructure.corspolicybuilder.setisoriginallowedtoallowwildcardsubdomains?view=aspnetcore-2.1) functionality on a multi-tenant service. I can do this via the `Configure()` method in my WebAPI, but not via the authentication blade in the portal (or AFAIK via resources.azure.com).
When I make the change in the `Configure()` method, the support for wildcard sub domains only applies to my custom route, not the .auth/* routes. This causes failures when the clients' tokens expire and we redirect them to .auth/refresh. If we explicitly add tenants to the list of allowed tenants, it appears to work.
Would it be possible to add support for wildcard subdomains to address the issue with .auth/refresh?
And here is a snip of the CORS `Allowed Origins` setting I'd like to make:
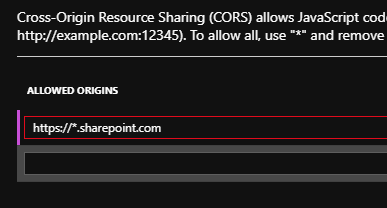
It would also be helpful if the Authentication Blade's `Allowed External Redirect Urls` setting supported wildcard subdomains:
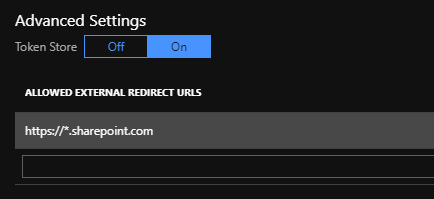
Thanks for considering this!
Contributor guide
Research direction
Start with the linked #620 discussion and its referenced comment, then review the CORS Allowed Origins and Authentication Blade Allowed External Redirect Urls requirements described here. Done means wildcard subdomains work for .auth/refresh as well as custom routes, and are supported in both portal settings requested by the issue.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- azure, csharp
- Domain
- authentication, cloud, security
- Issue type
- Feature
- Difficulty
- 5/5
- Estimated time
- Over a week
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 25/100