az container create cannot parse sas token as secrets
- Dominant language
- Python
- Stars
- 4.6k
- Forks
- 3.5k
- Avg merge
- 3d 2h
- Merged PRs (30d)
- 60
Description
> ### `az feedback` auto-generates most of the information requested below, as of CLI version 2.0.62
**Describe the bug**
I was trying to create an azure container instance from my image in acr. For some reason I want to have my sas token mounted as secrets. However it failed.
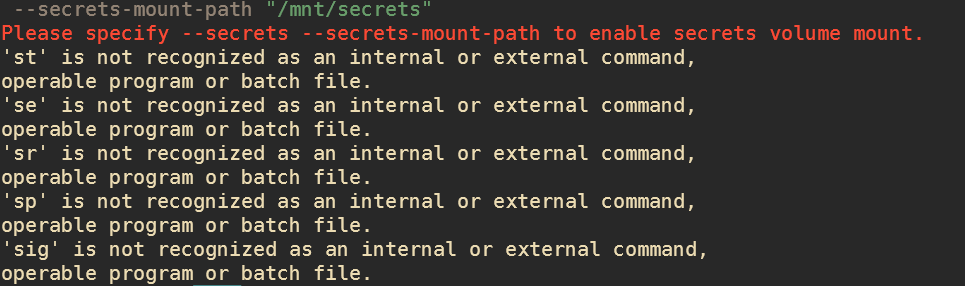
I think the reason of this might be the **&** and it was not protected by the quotation mark and interpreted as a new command. Tried use **\\** to escape it doesn't work. The cli command works fine if I replace the **&** with %26, but I don't think the sas token will work properly unless we transfer it back from %26 to **&** .
**To Reproduce**
az container create -n containername -g groupname --image "org.azurecr.io/containerimage:tag" --registry-username "acrusername" --registry-password "acrpassword" --secrets blobsas="?sv=2020-04-08&st=2021-08-06
....some sas here...%3D" --serects-mount-path "/mnt/secrets"
**Expected behavior**
A container should be create and the sas token should be mounted as a tmpfs volume
**Environment summary**
Install Method: MSI
CLI version: 2.27.1
OS version: Windows 10
Shell Type: Powershell
**Additional context**
Contributor guide
Assessment
This issue has not been assessed yet.