Altinn / Altinn/app-lib-dotnet
Better error message from validation of anti forgery token
- Dominant language
- C#
- Stars
- 8
- Forks
- 27
- Avg merge
- 1h 21m
- Merged PRs (30d)
- 7
Description
## Description
The anti forgery token validation currenctly produce a bad request without any further information about what is wrong. There is also limited logging making it very hard to identify where the error comes from . Developers naturally assume there is something wrong with the request they crafted and starts analysing that instead of potential cookies.
The issue doesn't come up too often, but it's usually a developer of an app or end user system testing the App API with Postman. If Postman for one reason or another have recorded/grabbed request cookies from a browser, the cookies triggers the anti forgery token validation, which fails. Identifying that the issue is cookies and not the body of a post request is impossible.
## Screenshots
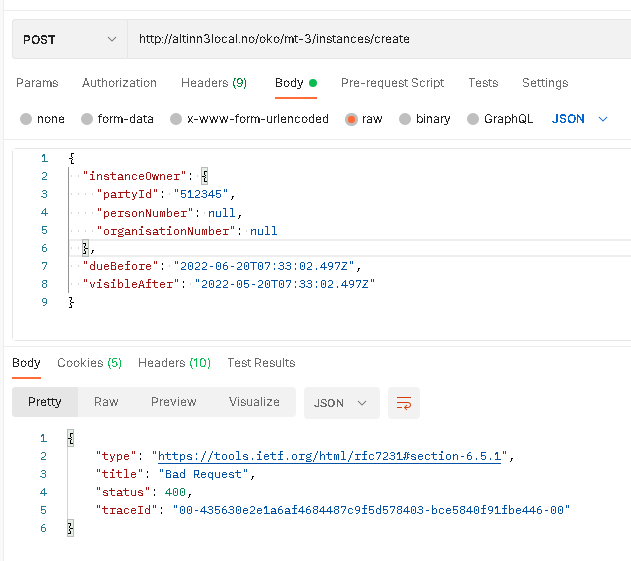
A developer would assume there is something wrong with their request. This is technically correct, but they would believe the issue is what they have in the body, headers or url. Not the cookies.
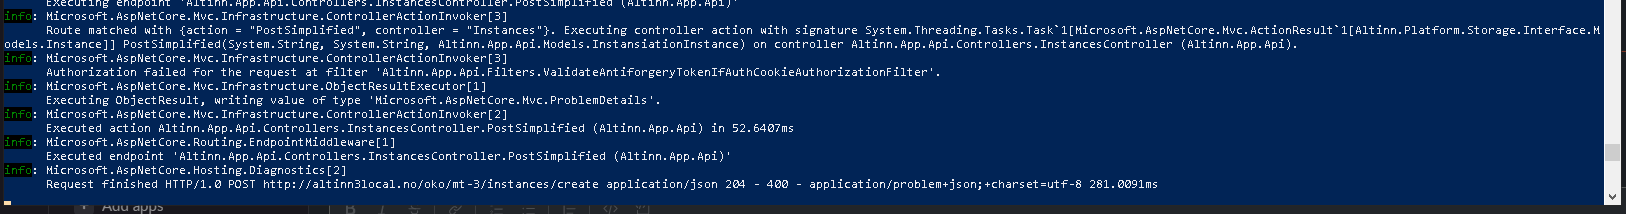
## Acceptance criteria
It's easier to see what's wrong.
## Specification tasks
- [ ] Development tasks are defined
## Development tasks
## Test
## Definition of done
- [ ] Documentation (docs.altinn.studio) is updated (if relevant)
- [ ] Technical documentation
- [ ] User documentation
- [ ] QA
- [ ] Manual test is complete (if relevant)
- [ ] Automated test is implemented (if relevant)
- [ ] All tasks in this userstory are closed (i.e. remaining tasks are moved to other user stories or marked obsolete)
Contributor guide
Research direction
Start by locating the anti forgery token validation path in the app-lib-dotnet code and reproduce the failure with a Postman request carrying browser cookies. The work is done when the resulting bad request and available logging make clear that cookie-related anti forgery validation caused the failure.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- csharp
- Domain
- backend, security
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Needs clarification
- Newbie friendliness
- 35/100