99x / 99x/serverless-dynamodb-local
Fix npm published version number
- Dominant language
- JavaScript
- Stars
- 621
- Forks
- 232
- PR merge metrics
- No merged PRs in 30d
Description
**Actual Behaviour**
If you run `npm audit`
```sh
$ npm audit
=== npm audit security report ===
# Run npm install --save-dev serverless-dynamodb-local@1.0.2 to resolve 1 vulnerability
SEMVER WARNING: Recommended action is a potentially breaking change
┌───────────────┬──────────────────────────────────────────────────────────────┐
│ Moderate │ Prototype Pollution │
├───────────────┼──────────────────────────────────────────────────────────────┤
│ Package │ node.extend │
├───────────────┼──────────────────────────────────────────────────────────────┤
│ Dependency of │ serverless-dynamodb-local [dev] │
├───────────────┼──────────────────────────────────────────────────────────────┤
│ Path │ serverless-dynamodb-local > dynamodb-localhost > rmdir > │
│ │ node.flow > node.extend │
├───────────────┼──────────────────────────────────────────────────────────────┤
│ More info │ https://npmjs.com/advisories/781 │
└───────────────┴──────────────────────────────────────────────────────────────┘
```
It advises you to instal:
`npm install --save-dev serverless-dynamodb-local@1.0.2`
**Expected Behaviour**
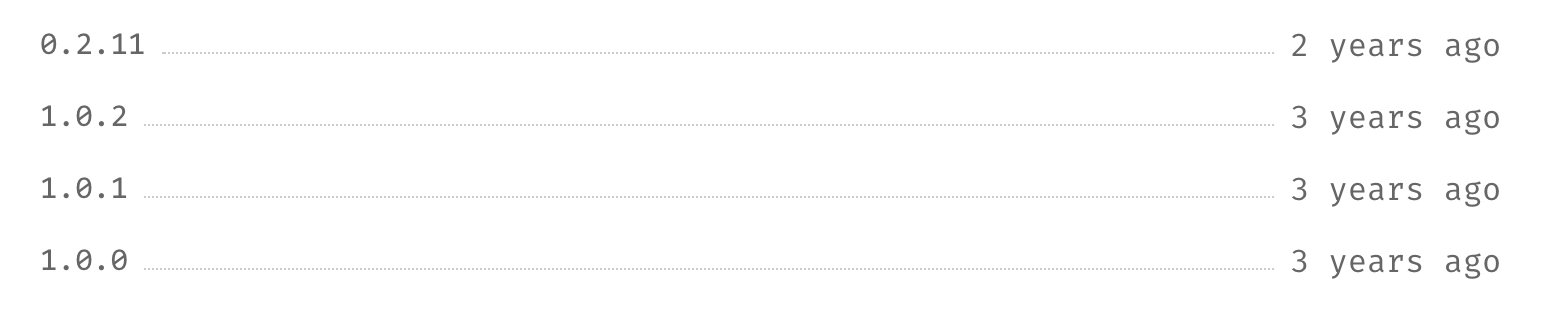
It should offer to install the verson `0.2.37` as that is the latest version of the package. This is because [npm registry version has `1.0.0`, `1.0.1` and `1.0.2` version published](https://www.npmjs.com/package/serverless-dynamodb-local?activeTab=versions) 3 years ago.
**Steps to reproduce it**
run `npm audit`
**Would you like to work on the issue?**
May be, it require npm publish access to fix this issue.
Potential options:
1) Depricate npm releases `1.0.0`, `1.0.1` and `1.0.2`.
2) Release a new version `1.2.38`
I know that option 2 is against how semver works. In this case publishing those `1.x` version has lead to this issue. However this will set things on the right track for future releases. Essentially you are doing a fake release to realign semver releases.
Contributor guide
Research direction
No repository file or test is named; start by reproducing the report with npm audit and checking the package's published version history. Review the two proposed registry actions and confirm completion when npm audit recommends the intended current package version instead of 1.0.2.
Written by the indexing model from the issue text.
Assessment
- Tech stack
- javascript
- Domain
- release
- Issue type
- Bug
- Difficulty
- 4/5
- Estimated time
- 3-5 days
- Activity status
- Stale
- Clarity
- Mostly clear
- Newbie friendliness
- 25/100